
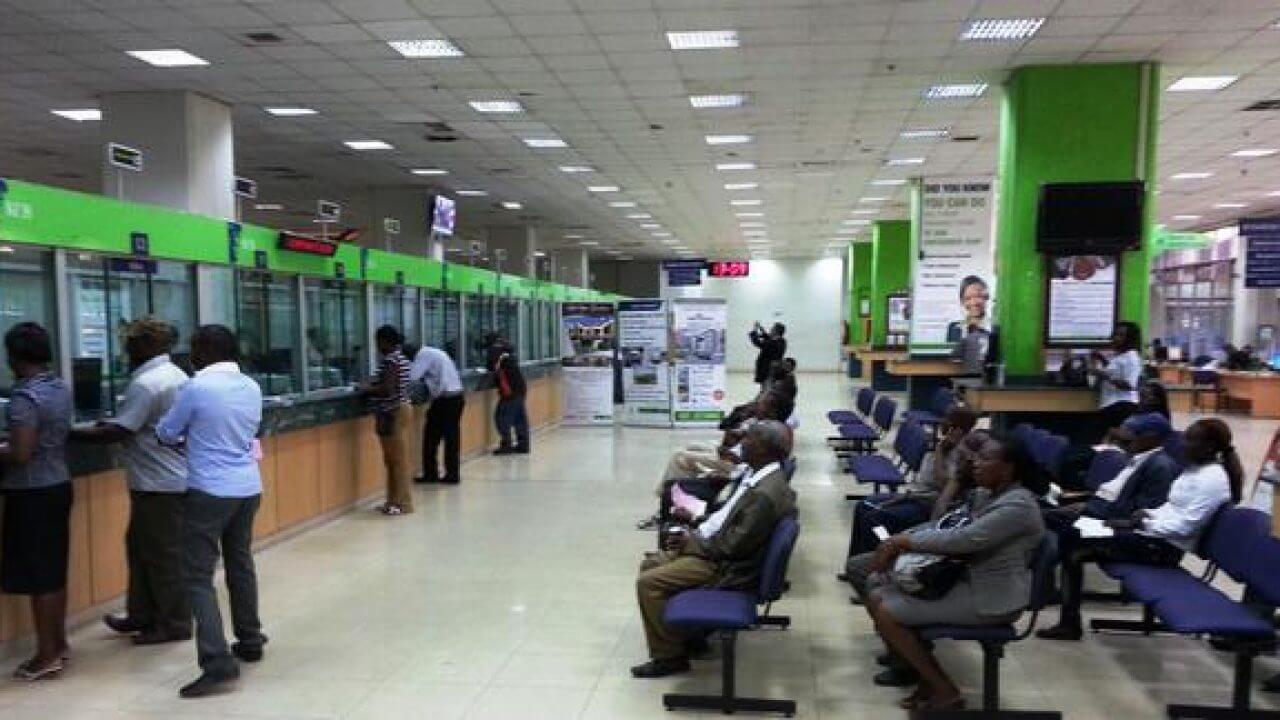
Nigeria’s banking sector is facing growing cybersecurity threats as criminal networks, sometimes allegedly assisted by bank employees and other insiders, exploit weaknesses in financial technology systems to divert billions of naira from customers and financial institutions.
From unauthorised withdrawals and compromised mobile banking applications to sophisticated attacks on bank servers, payment platforms and cryptocurrency exchanges, the rising incidents have renewed concerns about the safety of customers’ deposits and the ability of financial institutions to protect sensitive information.
A report published by Saturday PUNCH on November 7, 2026, highlights how ordinary bank customers, including elderly pensioners, have become victims of increasingly sophisticated fraud schemes, while major financial institutions continue to battle cyberattacks involving insiders and external hackers.
One of the incidents involved a 73-year-old Lagos resident, identified by the publication as Mrs Agnes Uwaila, whose name was changed to protect her identity.
The retired University of Lagos non-academic staff member reportedly lost approximately N3 million after visiting her bank to complain about difficulties accessing its mobile banking application.
According to a friend, the woman had approached the bank’s customer service department for assistance, where a staff member allegedly requested her personal identification number (PIN) to resolve the problem.
Days later, she began receiving debit notifications indicating that withdrawals were being made from her account. Within hours, approximately N3 million had reportedly disappeared.
The money represented her life savings and financial support from her daughters. Having retired after more than four decades of service at UNILAG, she depended largely on her pension.
The shock reportedly caused her to faint, after which she was taken to a hospital for medical attention.
The circumstances surrounding the alleged theft remained unclear, with concerns raised about possible compromise of her PIN, unauthorised access to her account or a breach involving the bank’s digital platform.
Another Lagos resident, identified simply as Shola, reportedly experienced a similar incident after visiting a different bank to complain about problems with its mobile application. She said criminals subsequently began withdrawing money from her account in small amounts.
She eventually involved the police, and most of the stolen funds were reportedly recovered.
The incidents illustrate the vulnerability of bank customers when personal banking information or digital credentials fall into the wrong hands.
Cybercriminals employ several methods to gain access to banking systems and customer accounts.
One common technique is phishing, in which fraudsters send deceptive emails, text messages, bank alerts or online links designed to trick customers into disclosing their passwords, PINs and other confidential information.
Malware is another major threat. These malicious programmes can infect computers and mobile devices, steal login credentials, monitor keyboard activities and provide attackers with remote access to compromised systems.
A technology staff member of a commercial bank, who spoke anonymously, explained that hackers could exploit outdated software, weak authentication procedures and poorly secured applications to penetrate banking infrastructure.
The source also warned that employees could unknowingly introduce malicious software into their organisations by downloading suspicious attachments or programmes.
However, cyberattacks are not always carried out entirely from outside financial institutions. In some cases, insiders allegedly provide criminals with access to sensitive systems or facilitate fraudulent transactions.
Cybercriminals may also target technology vendors, payment processors and other third-party organisations connected to banking infrastructure.
The report also draws attention to a major cryptocurrency security breach involving Binance, one of the world’s largest cryptocurrency exchanges.
According to the account, hackers allegedly used deceptive recruitment processes and malicious software to compromise the computers of software engineers working with the exchange.
An employee reportedly downloaded a compromised internet tool, while another engineer allegedly installed a malicious code repository after participating in what appeared to be a legitimate job interview.
The attackers subsequently exploited access to the affected systems.
On October 29, approximately 233.46 million XRP was reportedly transferred from five Binance internet-connected wallets to an address controlled by the attackers within four minutes. Other cryptocurrencies, including Bitcoin, were also allegedly withdrawn.
Reuters reported that the attackers continued moving cryptocurrency for nearly four hours after the initial theft, even as the exchange worked to secure its systems.
The report put the value of the cryptocurrency stolen in the operation at $6.3 billion.
A Nigerian cryptocurrency trader, Michael Efa, said the incident was unlikely to stop trading activities but predicted that the market could experience misleading buying signals following the security breach.
Although cryptocurrency exchanges and conventional banks operate differently, both depend heavily on secure digital infrastructure and the protection of sensitive access credentials.
One significant difference is that conventional bank transactions can sometimes be investigated, disputed and reversed through established banking procedures, while transactions on many decentralised cryptocurrency networks are generally irreversible once
The scale of financial fraud in Nigeria is reflected in figures contained in the Central Bank of Nigeria’s Payments System Vision 2028 document.
According to the figures cited in the report, Nigerian bank customers lost a cumulative N134.48 billion to fraud between 2020 and 2025.
Data from the Nigeria Inter-Bank Settlement System also showed that digital payment fraud and cyber-related losses reached N25.85 billion in 2025.
Although this represented a 51 per cent decline from the N52.26 billion recorded in 2024, the previous year’s losses were reportedly influenced by major incidents, including a single fraud event involving approximately N31.1 billion and coordinated attacks allegedly involving insiders.
The figures demonstrate that despite investments in digital security, financial institutions continue to face substantial threats.
Several Nigerian financial institutions have experienced significant cyber-related incidents in recent years.
SunTrust Bank Plc was reportedly targeted in multiple attacks over a three-year period, with suspects allegedly diverting more than N800 million through breaches of its computer systems.
On August 6, a 47-year-old suspect identified as Ugochukwu Eze, popularly known as Amazon, was arraigned before the Federal High Court in Lagos by operatives of the Department of State Services.
He was subsequently granted bail on September 14, according to the report.
Another major incident involved Wema Bank, whose computer systems and servers were allegedly compromised in January 2025.
The attackers reportedly manipulated financial data, authorisation procedures and internal transfer systems to divert approximately N8.5 billion.
In May 2025, the Economic and Financial Crimes Commission arraigned three bank employees and four external individuals over their alleged involvement in the incident.
Although the defendants pleaded not guilty, a Lagos Special Offences Court sitting in Ikeja later convicted one of the bank employees, Ihechukwu Asiegbu, and sentenced him to three years’ imprisonment in November 2025 for unauthorised access to the bank’s computer system to facilitate the theft.
First Bank also reportedly initiated legal proceedings in 2024 to recover approximately N40 billion allegedly diverted by an employee attached to its head office team in Iganmu, Lagos.
The employee was accused of transferring the funds into 98 beneficiary accounts, including an account belonging to his wife.
The bank reportedly alerted the Nigeria Police Force on March 25, 2024, and obtained court orders to block hundreds of accounts suspected to have received the diverted funds.
In another case, the EFCC prosecuted a former Globus Bank information technology employee over the alleged theft of N3.5 billion through unauthorised access to the bank’s systems.
The commission reportedly recovered approximately N1.2 billion during investigations, although the accused employee denied the allegations.
The report also recalled the arrest of Femi Salau in 2021 over an alleged N1.87 billion theft involving the Flex-Cube Universal Banking System. Police investigators described him as the alleged leader of a syndicate specialising in attacks on banking and corporate computer systems.
Hope Payment Service Bank also suffered a major cybersecurity incident in July 2024, with reported losses ranging between N6.5 billion and N10 billion.
Court-related charges and prosecution figures reportedly placed the alleged losses as high as N9.68 billion to N10 billion.
In October 2024, the Federal High Court in Abuja ordered the freezing of 818 bank accounts across commercial banks and digital financial institutions following an application by the Inspector-General of Police.
The order was intended to help intercept and recover funds allegedly diverted during the incident.
The case highlights the challenges involved in tracing and recovering stolen money after cybercriminals move funds through multiple accounts.
The Central Bank of Nigeria has also raised concerns about cybercriminals impersonating the apex bank to obtain personal information from unsuspecting members of the public.
In a statement signed by its Acting Director of Corporate Communications, Hakama Ali, the CBN warned that fraudulent emails and online messages were being circulated under the false claim that they originated from the institution.
Some of the messages reportedly contained suspicious links and misleading information about the bank’s leadership, licensing activities and policy decisions.
The regulator advised Nigerians not to click on suspicious links or disclose personal information through unverified websites.
It also urged members of the public to confirm official communications through the CBN’s website and recognised media organisations and report suspected fraudulent messages to law enforcement authorities.
Separately, the Nigeria Data Protection Commission commenced an investigation in April 2026 into an alleged data breach involving Remita Payment Services Limited, Sterling Bank and other entities.
The development further highlighted concerns about the protection of personal information held by financial institutions and technology service providers.
Under Section 40 of the Nigeria Data Protection Act, organisations that experience a personal data breach likely to pose risks to the rights and freedoms of individuals are required to notify the Nigeria Data Protection Commission within 72 hours of becoming aware of the incident.
Where a breach is likely to create a high risk for affected individuals, the organisation is also expected to communicate the incident to them without delay.
Such communication should clearly explain what happened and provide information about steps customers can take to reduce possible harm.
However, concerns remain that some financial institutions may prefer to handle cybersecurity incidents internally rather than promptly disclose them to customers and the wider public.
A former senior management employee of a new-generation bank, identified as Amos Oderinlo, explained that cyber-related theft could expose financial institutions to significant financial and reputational damage.
He said banks might be required to refund customers where investigations establish that losses resulted from failures on the institution’s part.
However, he noted that responsibility could differ where a customer’s negligence or failure to follow security advice contributed to the incident.
David Odes, a cybersecurity expert and founder of Web Security Lab, explained that attackers do not necessarily need to defeat every security layer protecting a bank before gaining access to its systems.
According to him, a single weakness could provide an entry point into a much larger network.
Such weaknesses could include employees with excessive system privileges, outdated software, poorly secured applications and vulnerabilities in banking platforms.
He particularly identified Application Programming Interfaces (APIs), which allow mobile and web applications to communicate with backend systems and other services, as potential targets when security controls are inadequate.
Odes also warned that vulnerabilities could exist within third-party vendors and service providers connected to financial institutions.
He explained that once attackers gain an initial foothold, they may spend days or weeks studying an organisation’s infrastructure, moving between systems, increasing their access privileges and identifying critical platforms.
The expert stressed that banks must pay attention to insider threats and ensure that employees only have access to systems required for their official responsibilities.
He also cited concerns raised by EFCC Chairman Olanipekun Olukoyede about an investigation involving six financial institutions, where employees allegedly collaborated with external attackers.
According to the account, some insiders allegedly connected devices to banking systems, enabled individuals outside Nigeria to remotely control the systems and assisted in moving stolen funds.
Odes said banks should strengthen their ability to monitor activities across their networks, including employee authentication, privileged accounts, network traffic, API requests and unusual transaction patterns.
He recommended regular penetration testing, vulnerability assessments, independent security audits and properly staffed Security Operations Centres.
He also advocated network segmentation, restricted access privileges and Zero Trust security principles to prevent the compromise of one account or device from exposing
An ethical hacker identified only as Khelly said human behaviour and inadequate cybersecurity awareness remained major factors contributing to attacks on organisations.
He explained that careless employee actions, including connecting unidentified flash drives to company computers, could introduce malware into sensitive systems.
He also identified disgruntled employees as potential insider threats, noting that workplace dissatisfaction, resentment and perceived unfair treatment could sometimes motivate individuals to expose confidential information or assist attackers.
Khelly urged financial institutions to provide regular cybersecurity training for employees, establish clear security procedures and monitor their systems continuously.
He further advised organisations to restrict the use of personal computers for official work and ensure that external storage devices are properly checked before being connected to company systems.
Oladipo Gbolahan, a data product manager and AI product strategist, described multibillion-naira cyber thefts as both an operational crisis and a financial setback for affected institutions.
He explained that security breaches force organisations to divert resources from product development and other business activities towards investigations, system recovery and damage control.
He also warned that the consequences extend beyond the immediate financial losses, as customers may lose confidence in digital banking services.
According to him, financial institutions should assume that login credentials could eventually be compromised and design their systems to limit the damage through restricted access, transaction limits and real-time artificial intelligence-powered fraud detection.
Gbolahan also called for clear ownership of sensitive datasets, regular access reviews and prompt communication with customers whenever security incidents occur.
He stressed that cybersecurity should be treated as a board-level responsibility rather than an issue left exclusively to information technology departments.
The growing number of reported cyber incidents underscores the importance of protecting personal banking information.
Customers should take the following precautions:
- Never disclose ATM PINs, mobile banking passwords, one-time passwords (OTPs) or other confidential credentials to anyone.
- Avoid clicking suspicious links received through SMS, email or social media.
- Download banking applications only from trusted and official app stores.
- Do not install unfamiliar software or applications from unverified sources.
- Activate transaction notifications and regularly review account statements.
- Contact the bank immediately through its verified customer service channels when suspicious transactions occur.
- Report unauthorised withdrawals promptly and request an investigation.
- Avoid conducting banking transactions through public or unsecured Wi-Fi networks.
- Never assume that someone is a genuine bank employee simply because they claim to be calling from the bank.
Customers who suspect that their accounts have been compromised should immediately contact their banks, request appropriate restrictions on affected digital channels and report the incident to the relevant authorities.
As Nigeria continues to expand digital financial services, the security of banking infrastructure will remain central to public confidence in the financial system.
The increasing sophistication of cybercriminals means that protecting customers’ money will require more than advanced technology. Financial institutions must strengthen internal controls, improve employee accountability, secure third-party connections and communicate transparently when breaches occur.
For millions of Nigerians who depend on banks to safeguard their pensions, salaries, business proceeds and lifetime savings, the challenge is no longer simply about convenient digital banking. It is about ensuring that their money remains safe.